Arthur Besse
cultural reviewer and dabbler in stylistic premonitions
- 16 Posts
- 87 Comments
Joined 5 years ago
Cake day: January 17th, 2022
You are not logged in. If you use a Fediverse account that is able to follow users, you can follow this user.

fyi, the news story which this meme is premised on turned out to be a hoax.
none of the claims that there was a measurable drop in inauthentic social media activity as a result of the strikes on yandex datacenters held up when i tried to verify them. one of the graphs supposedly demonstrating it was obviously AI-generated and had dates in the future, while another was a cloudflare graph showing a drop in bot traffic but the bot there was solely yandex’s search engine web crawler traffic.
it’s remarkable how many people continue to believe it.

 5·5 days ago
The new edition, known as TUXEDO OS “Continuous Debian,” replaces the distribution’s traditional Ubuntu foundation with Debian Testing. The change denotes a significant shift for TUXEDO OS, which is developed by German Linux hardware manufacturer TUXEDO Computers.
[…]
Unlike Debian itself, which periodically promotes its Testing branch to Stable, TUXEDO OS will remain permanently based on Debian Testing.
🤔
https://www.debian.org/security/faq#testing currently says:
Q: How is security handled for
testing?A: Security for testing benefits from the security efforts of the entire project for unstable. However, there is a minimum two-day migration delay, and sometimes security fixes can be held up by transitions. The Security Team helps to move along those transitions holding back important security uploads, but this is not always possible and delays may occur. Especially in the months after a new stable release, when many new versions are uploaded to unstable, security fixes for testing may lag behind. If you want to have a secure (and stable) server you are strongly encouraged to stay with stable.
I wonder if TUXEDO Computers plans to be shipping security updates themselves faster than Debian
testingdoes?
LPEs are not RCEs
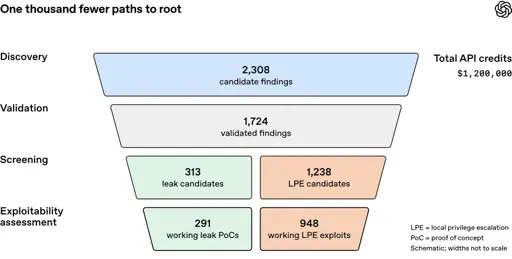
They didn’t say they were, the post is very clear about the the 948 vulns they’re talking about being LPE.
If it’s a bunch of local jvm consoles or vi escapes into shell
if it was that, they wouldn’t be “Linux LPEs”. These are clearly kernel bugs they’re talking about.
And again, stop taking OpenAI at their word about security.
OpenAI is full of shit about a lot of things but I doubt they’re lying about having working exploits for these Linux bugs.
 1·6 days ago
I literally downloaded the one you’re referring to and replaced the old one with it, without doing any editing of it
i guess your instance must have downscaled it then
Nah, I’ve had this one since the 2010s. There was no AI upscaling back then.
There was, actually: the SRCNN paper was in 2014, and widely accessible tools using CNNs for upscaling became available soon after (such as waifu2x in 2015 and Neural Enhance in 2016).
There are some other image scaling algorithms which could possibly maybe produce artifacts like that without a neural network but I am relatively sure that the image you posted was “AI upscaled”.
Now that this comment has linked you to a full-res version of this image, I hope you’ll edit the post
Already did.
The version you’re linking to now is at least readable, but still full of compression artifacts and is a third of the resolution of the version @PM_ME_VINTAGE_30S@anarchist.nexus linked to.
Sure, you can generate a list of places to start testing, but each of those has to be validated, reproduced, documented and understood before it’s confirmed
i guess you didn’t actually read the blog post this article links to? The number in the headline (948) is the number of LPE bugs which they say they validated and reproduced and developed exploits (and patches) for.
I am baffled as to how you could think it was a good idea to post this image you posted.
Some of the text is entirely unreadable; it was obviously scaled down too far and then scaled back up using AI upscaling:

Now that this comment has linked you to a full-res version of this image, I hope you’ll edit the post. (I’m linking to what you originally posted in this comment so people can see why this post got downvotes after you do.)
also imo when linking to a meme with an abridged version of a quote it’s nice to include a link to the unabridged version also. So: here is the text and pdf scan of the Letter from Birmingham Jail.
what do you mean?
Something else AI’s ruining…
can you explain what you mean by this? are they ruining linux by revealing its bugs at a much faster rate? or ruining the security research field by depriving researchers of the challenge and enjoyment of finding these bugs themselves?
repeating myself from a previous thread: of all the things i hate about LLMs, getting vulnerabilities in important software like linux discovered and fixed is not one of them
(although, as i said elsewhere in this thread, i find it unlikely that openai is actually disclosing all of the bugs they find 😬)

it’s a bit odd how openai’s blog post makes it sound like security bugs in Linux fall in two categories, info leak and local privilege escalation. i would guess that they probably did also ask their model to find some RCEs, but they’re selling those to exploit vendors (or perhaps to intelligence agencies directly?) rather than blogging about fixing them.
 4·7 days ago
came here to post the same but since you already did i had to fix the image:

Developed in partnership with the GrapheneOS Foundation, the leading nonprofit in advanced mobile security, the device reflects Motorola’s commitment to bringing cutting-edge security to everyday users across the globe.
everyday users who can afford a $1600 phone, that is 🙄
fyi, the news story which this meme is premised on turned out to be a hoax.
none of the claims that there was a measurable drop in inauthentic social media activity as a result of the strikes on yandex datacenters held up when i tried to verify them. one of the graphs supposedly demonstrating it was obviously AI-generated and had dates in the future, while another was a cloudflare graph showing a drop in bot traffic but the bot there was solely yandex’s search engine web crawler traffic.
it’s remarkable how many people continue to believe it.
 1·11 days ago
In the spirit of open-source OP asked if people want to contribute their time. You wouldn’t flame any other foss project this hard for simply being unfinished.
asking strangers to review your LLM outputs without informing them that some (or in this case, most) of it has never been reviewed by any human before, is not at all in the “spirit of open-source”. This website continues to be very misleading: it says “Learn math and science by doing. Bite-sized, hands-on lessons. Drag, predict, and solve your way to real understanding. Free for everyone.” and has a “Start learning” button. The disclaimer which OP added on the About page absolutely needs to be moved to the front page, where everybody will see it before they see a pitch implying that this is ready to go.
@kiarash@lemmy.world when i undeleted your post before, after you added the “less than a third” disclosure on the About page, I told you in a PM that that was insufficient and I see now you have still not fixed it so I am sorry but I am going to delete this post again. Send me a PM if/when you make the disclosure of what this actually is far more prominent. I suggest showing your agent my comments and asking it if this is reasonable and if your disclosures are sufficiently prominent.
 4·11 days ago
https://www.spacejam.com/2021/ is not much different tho
 4·11 days ago
I was really expecting your last paragraph to say the opposite of what it says 😂

I don’t have this device but, on behalf of everybody who does and will be able to run mainline linux on it in the future due to your work: thank you!
i’m not sure but i think that detector might be detecting an openai-specific watermark which indicates that it was not a ring camera’s slopification but actually a fake. or maybe the detector itself is fake and the image is real, who knows.
in any case, fuck this meme for normalizing ring cameras and acting like they’re cool and ok - there are lots of reasonable ways to do video surveillance of your own home without sending all of the data to amazon and the cops and the various other private and government entities they share it with.
people with ring cameras should be shamed.
I agree. I’ll make the modifications later. Thank you.
Thanks, glad to hear it.
How much later, though? If it’s not soon, I think I will delete this post for now (i’m an admin on the home instance of this community). You can still edit it while the post is deleted but only you and mods and admins will be able to see it; send me a message after your edits are made and I’ll undelete it.
To be clear what I am asking for is an early/prominent/clear disclosure, both on the website and in the body of this lemmy post, of the percentage of the lessons which you estimate have not yet been carefully read by you (or presumably anyone else).
Thank you, and I hope this isn’t too discouraging!







imo this community should have a rule against posts promoting new primarily-written-with-an-LLM software projects. as an admin, i’ve deleted a few myself when there are reports of them and the mods aren’t resolving them.
banning all AI-assisted software is obviously no longer reasonable now that many large and old projects are using it (with varying levels of care…) but I don’t think we actually need a very firm definition of “slop” to be able to say some things clearly are slop and some AI-involved things clearly aren’t. When in doubt about if something is of sufficient quality that we should keep it here, the age of the project and the number of developers involved are useful secondary metrics.
@gary_host_laptop@lemmy.ml created a new community which I think should be linked in the sidebar here as an alternate place for sharing these things. How about this for a rule (in the !opensource@lemmy.ml sidebar)?
note that the word “slop” is intentionally absent from my proposed rule (and from name and description of the community) - the point is that this is a place for people to share their AI-created software, regardless of if it is 100% vibe coded or is actually high-quality “agentic engineering” - only time, review, and users will ultimately tell which category many of these new things fall into. But enough of it is slop that we shouldn’t have this community flooded with it, imo.
cc @CrypticCoffee@lemmy.ml @Lettuceeatlettuce@lemmy.ml @kevincox@lemmy.ml