- 80 Posts
- 104 Comments


 9·3 days ago
With any luck Johnson will fade quickly into obscurity and this will be one of the last times this asshole makes the news.
He can go back to monitoring his son’s phone to make sure he doesn’t look at any pictures that would make the baby Jesus cry.
 1·3 days ago
What’s your concern with a new printer? In case 1, once set up and working how is a company going to introduce malicious features when the printer has absolutely no Internet access?
You’re overthinking this with 2 & 3. All you need is to block all Brother Internet traffic.
Set up a static DHCP IP for the printer in Openwrt and create firewall rules to drop all WAN packets to/from that IP.
If you want to see evidence those packets are being dropped in real time use tcpdump. When watching LAN traffic you will see the printer sending packets to the WAN interface (they won’t get there) but will never see a response directed back to the printer.
I have a Brother printer (plus cameras & TVs) and an Openwrt router set up that way and have had zero issues.
Still funny

Election day 2026: The gift that keeps on giving.
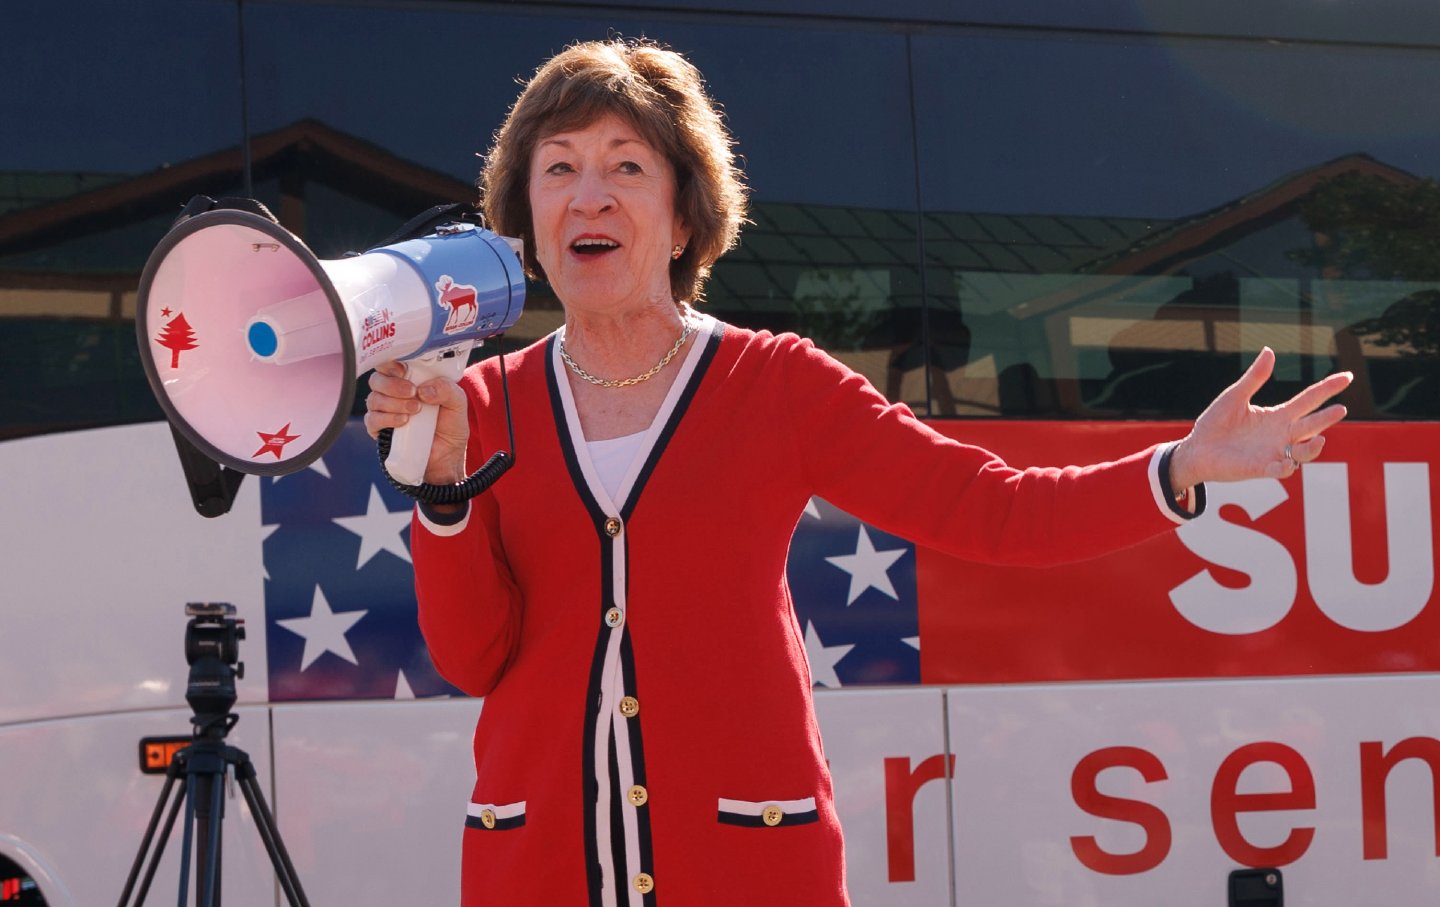
Despite her whines, the reality is Collins only broke with Republicans when she was sure it would make no difference to the vote outcome. She made damn sure to toe the party line the rest of the time.
And she’s wrong, sometimes it is enough: Voters have had enough of Susan Collins.

“They want to, what is it? Save democracy by destroying democracy,” Trump Jr. said of Democrats. “They wanna pack the Supreme Court. They wanna make Ohio a state, make D.C. a state, have permanent one-party rule.”
Every single accusation is an admission. The Grand Old Pedophiles are terrified of the majority and the return of the rule of law.

Republican lies work so well because they pander to Magats - the most uneducated, stupid, and uniformed voters, and they repeat the exact same lies again and again. Just because people here are generally informed does not mean Bubba in BumFuck, Tennessee is.
Joseph Goebbels: “If you tell a lie big enough and keep repeating it, people will eventually come to believe it.”
The same thing goes for repeating the truth. “Trump Rapes Children!” should be shouted each and every time his name is mentioned.
Translation: This is working just as the child rapist intended - transferring wealth from ordinary Americans to the 1%, exactly the same as his tariffs.

 17·23 days ago
An MSN aggregation link for a article on replacing Google? Here’s the direct Android Police link:
 14·25 days ago
He had plenty of long waits for appointments, but facts and reasoning weren’t involved.
Case in point: A 3 month wait in Canada - caused by universal healthcare = healthcare rationing = bad. That same 3 month wait in the U.S. = Freedom!
My brother, staunch Republican asshole, didn’t want universal healthcare because he might have to wait longer for an appointment.
It didn’t matter that it would cost less, have better outcomes, and people die without it. It was only about his convenience.

I had the same setup and the same problems with VPN (in my case Wireguard) server availability. While looking for a solution I realized I was trying to solve an architecture problem with software.
Instead of trying to find a software solution to work around my WG server uptime issues, I moved the Wireguard endpoint to an OpenWRT router. Now if my router is up, my WG endpoint is up and my network is accessible. I’ve been running this configuration for years and it has been 100% accessible.
I’m comfortable with the security of WG - open ports for WG endpoints are invisible to network scanners because they do not respond at all and appear closed unless they are sent the the correct key. Even if an attacker has some way of know a WG peer is listening on a specific port, cracking a 256-bit key would take trillions of years. I was then free to choose a remote access application without worrying about remote attackers gaining access to my servers because of some company’s failed security.
FOSS VNC server apps work OK, but I found them somewhat limited so I added NoMachine as my primary option and run both. It’s a commercial app but it’s free, and is one of the only closed source app I use. It can be run 100% locally (although they have a paid option that uses their servers). It allows full control over your servers including file transfer and audio.
Doesn’t check all your boxes, but it comes close.

Trump:
“If people get sick in the audience, they leave them alone. You know what they call them? Collateral damage,” He then pointed out someone in the crowd. "If that person right over there, he looks like s— actually. He looks like he’s ready to have a heart attack. " "If he actually had a heart attack, you know what my doctors would do, they would follow the president and leave him alone. “I’ve got like six ambulances and they won’t use one for anybody else.”
What a vile man.
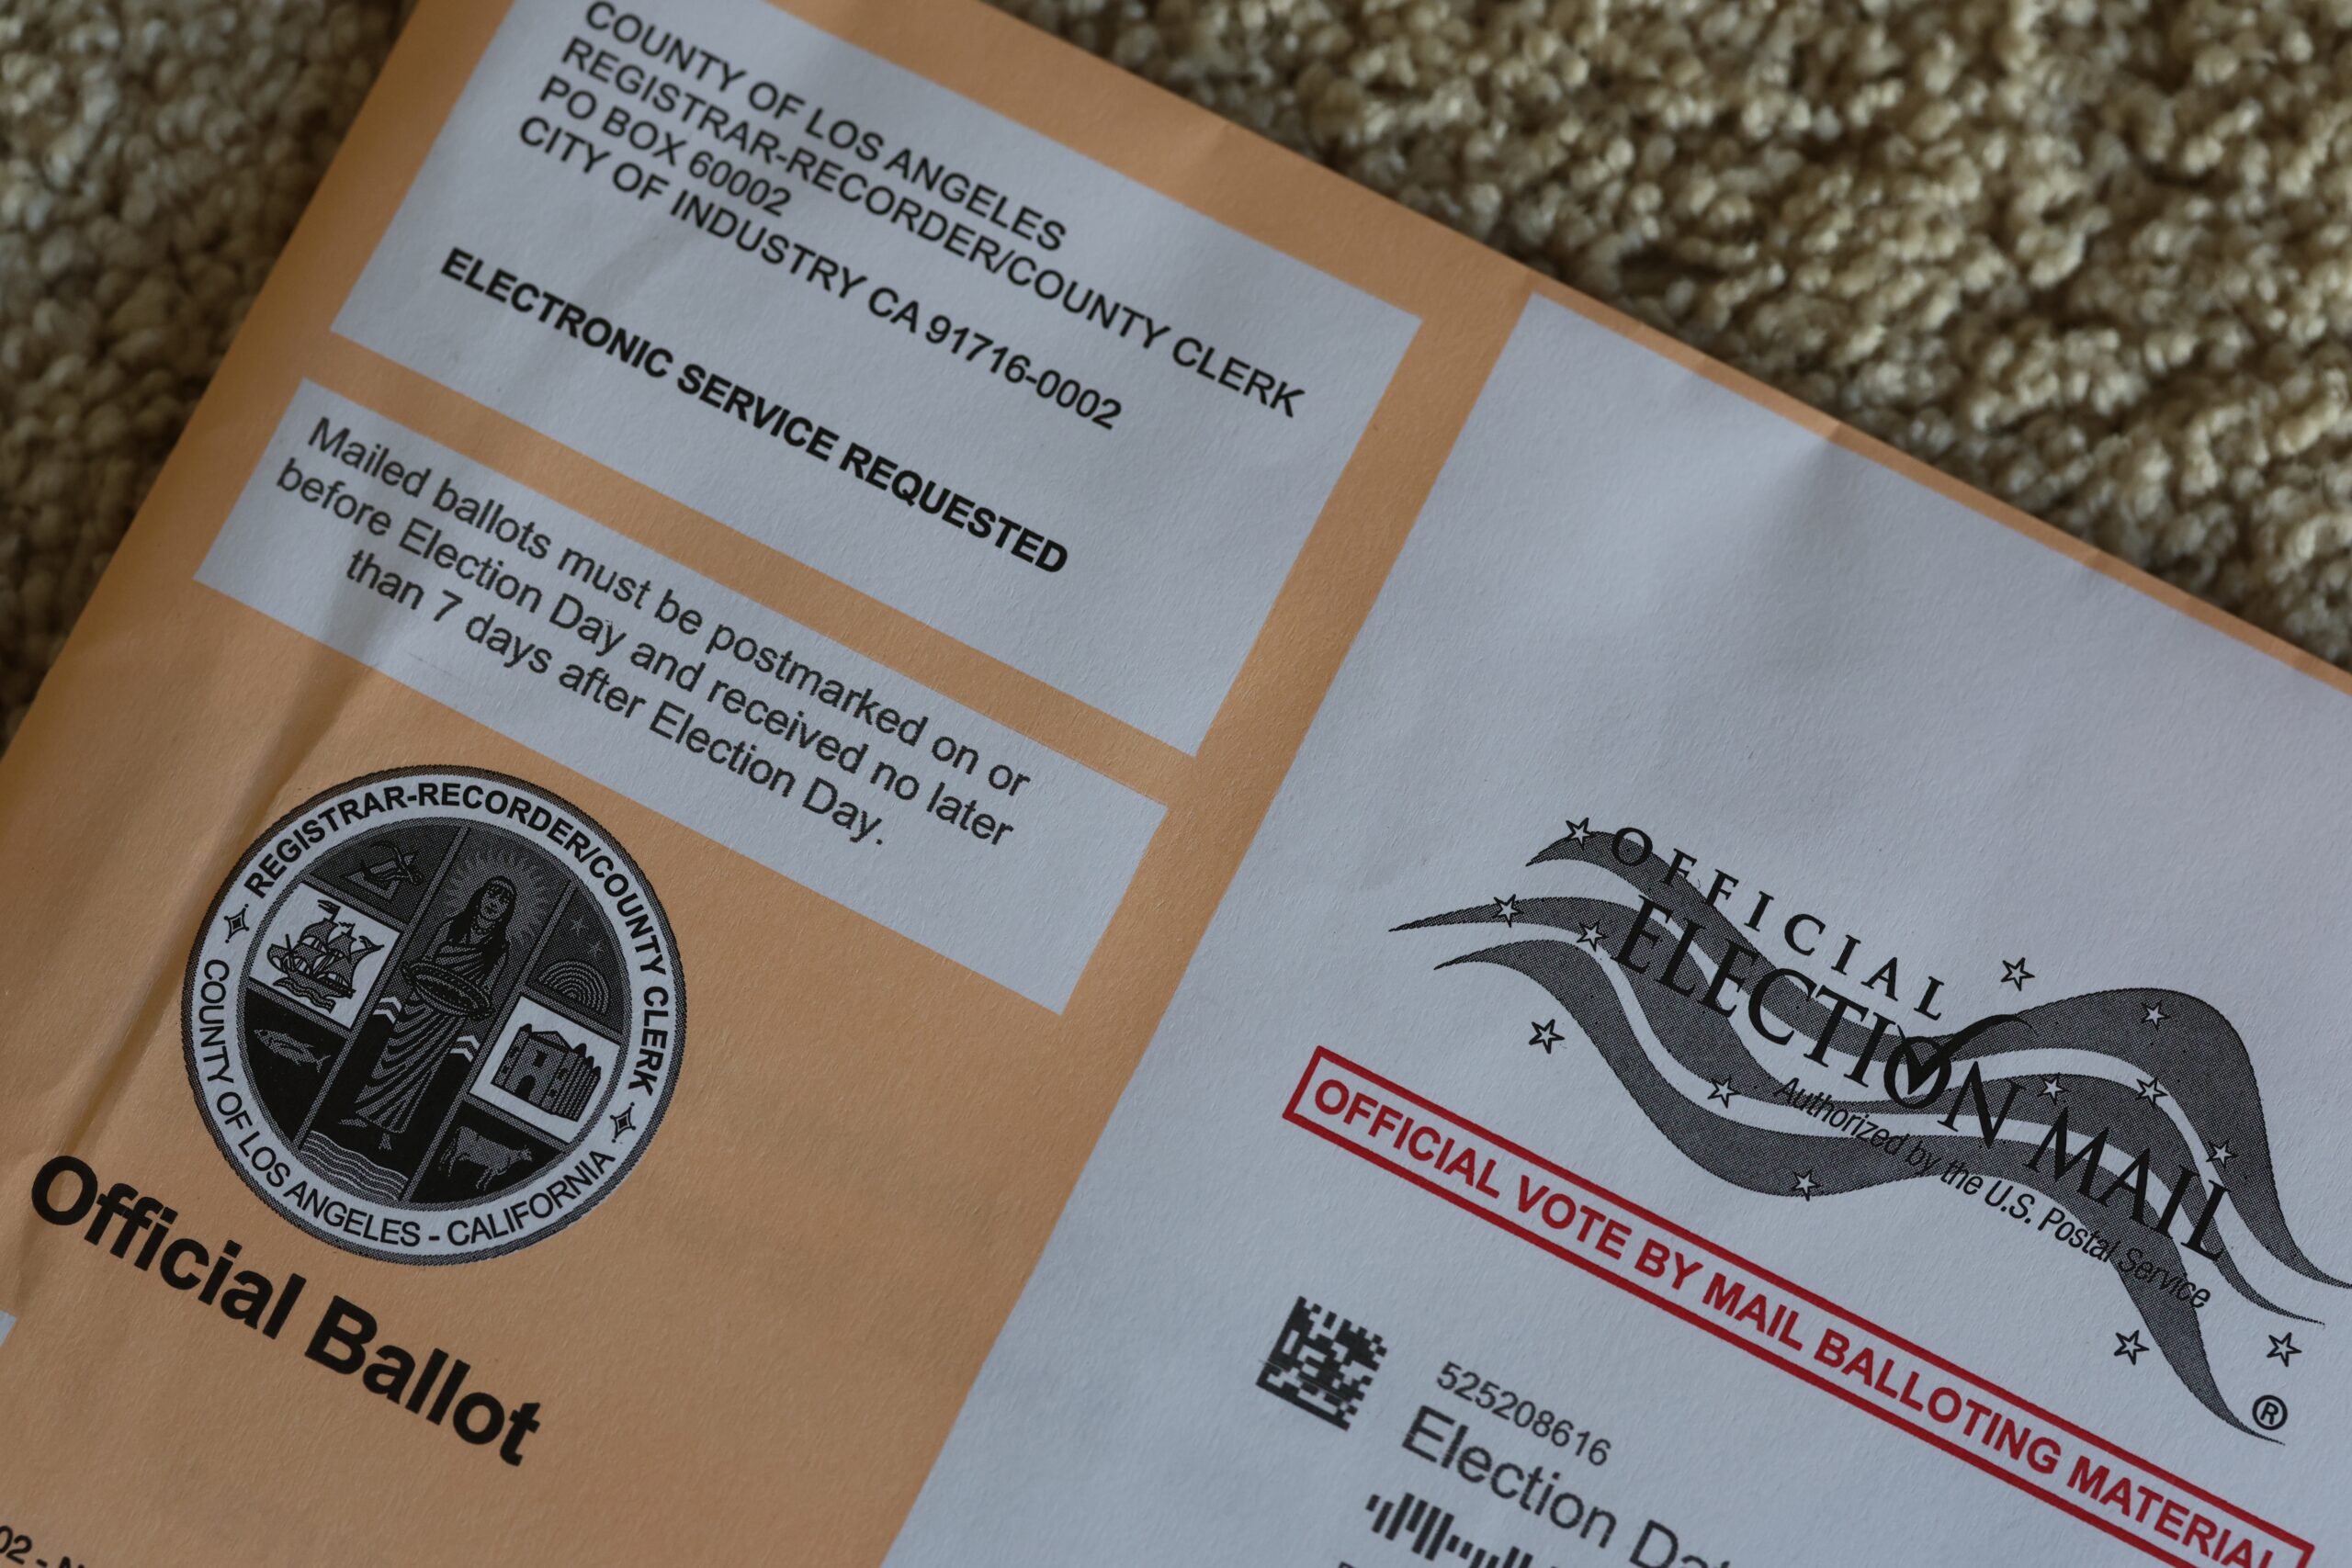
It is extraordinarily rare, so rare that even the ultra-right wing Heritage Foundation identified only 89 cases nationally since 2000. It is 100% Magat feed and distraction from the fact POTUS is a child rapist.

More Trump generated propaganda for the Magat class. Gotta keep people from focusing on the fact that Trump rapes children.
Alito doesn’t want religious liberty, he wants religious tyranny. The U.S. is not a theocracy, at least not yet, and it is horrifying this clergyman is in the highest level of power.
Wikipedia:
Religious abuse is abuse administered through religion, including harassment, humiliation, spiritual abuse, or religious violence. Religious abuse may also include the misuse of religion for selfish, secular, or ideological ends, such as the abuse of a clerical position.





That is infuriating and I’d do the same.
Plenty of reports of devices like LG TVs acting as gateways to external devices and LG in particular seems to be a privacy nightmare. I bought a couple of appliances that advertised their smart features only to find LG’s app was required. That app actually required both Internet access AND my exact location at all times to function at all! I shut it all down and disconnected everything from wifi.
You may be right to be concerned even about printers though. At some point we’re going to be reading about some built-in AI hacking other network devices for Internet access and transmitting our private information to the world.